A data leak happens when systemic security oversights, social engineering, or technical vulnerabilities expose sensitive records to unauthorized actors. Attackers use vectors ranging from phishing campaigns and credential brute-forcing to exposed cloud storage and unpatched software flaws. The financial consequences remain catastrophic, carrying an average organizational remediation cost of $4.88 million.
A data breach occurs whenever sensitive, protected, or confidential information is accessed, stolen, or exposed without authorization. Whether the incident targets login credentials, credit card details, medical records, or government identifiers, any personal, financial, or confidential information can be a target when enterprise defenses falter.
How Data Leak Incidents Happen Across Modern Networks
Attackers break into private corporate databases through a combination of:
- Social engineering
- Automated credential cracking
- Infrastructure misconfigurations
In a standard enterprise deployment, legitimate personnel query central databases using encrypted sessions, but external threat actors bypass these boundaries by manipulating employee trust.
Method 1 involves phishing, where an attacker sends a deceptive email containing a link to a fake login portal. Once an employee inputs their credentials, the attacker collects the account access instantly. Method 2 bypasses authentication through brute force attacks, where automated tools cycle through millions of common passwords against exposed login portals until one matches.
Method 3 relies on malicious attachments disguised as an routine invoice; opening the document installs stealth malware that quietly captures records from infected workstations. In more aggressive scenarios, ransomware encrypts the entire database and forces victims to pay hefty ransoms in Bitcoin for decryption keys.
System architecture mistakes and human disloyalty create equally devastating entry points. Organizations adopting modern infrastructure frequently suffer exposure when engineering teams configure cloud storage buckets as public, instantly leaking confidential assets to the open internet. Teams managing these architectures often reference Cloud Security 2024: Shared Responsibility for Data Protection to clarify where vendor safeguards end and internal responsibilities begin.
Internal operators also cause direct harm; a disgruntled employee can bypass firewalls entirely by copying restricted trade files directly onto a USB drive. Attackers also scan public networks for unpatched software, targeting known vulnerabilities left unaddressed by negligent IT maintenance. Historical incidents at Yahoo, Equifax, and Facebook prove that scale offers zero defense against these vectors; no organization is immune.
The immediate fallout extends far beyond internal operational downtime. TechVision Animated puts the average cost per breach in 2024 at $4.88 million.
Once attackers siphon corporate records, they liquidate the inventory on illicit dark web markets. Prices fluctuate based on depth and identity utility, scaling from thousands of dollars for basic email-and-password combos to tens of thousands of dollars for complete Social Security number databases.
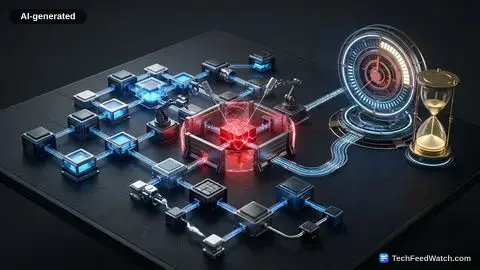
The investigative timeline magnifies these damages: companies require an average of 287 days to detect and contain a breach. This long latency leaves customers vulnerable to identity theft, ruins commercial reputation, and triggers regulatory penalties that can reach up to 4% of revenue.
For smaller enterprises, the damage is frequently terminal: 60% of small businesses close within 6 months of a major cyber attack. The ongoing threat environment documented in Data Breaches June 2026 Show Evolving Cyber Threats shows that attackers continue to refine automated exfiltration tooling.
Preventing unauthorized exposure demands active friction at every network tier. Enforcing multi-factor authentication ensures that stolen passwords remain useless without physical device verification codes. Comprehensive data encryption transforms stored and moving plain text into unreadable ciphertext, nullifying the value of captured databases lacking explicit decryption keys.
Organizations operating across integrated financial networks, such as those governed by Open Banking: Data and Trust Drive Personalized Finance, rely heavily on programmatic verification routines. Continuous software patching eliminates exploitable system flaws before attackers discover them, while real-time security log monitoring flags anomalous traffic patterns, halts brute-force attempts mid-execution, and alerts defense squads before exfiltration begins.