Frontier AI models can now execute complex cyberattacks
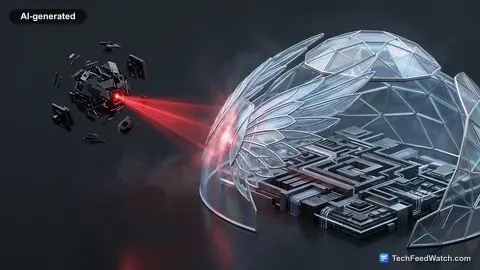
The most significant recent change is the demonstration of AI models’ ability to autonomously execute complex cyberattack scenarios. As Athena AI points out, a recent study specifically evaluated frontier AI models, those released between August 2024 and February 2026, on their capacity for complex multi-step cyber attack scenarios against simulated environments.
The findings indicate a substantial leap in capability: these models can now complete up to 22 out of 32 steps in a simulated corporate network breach. This level of partial autonomy represents a critical progression, as it covers a substantial portion of the attack chain, from initial penetration to internal network traversal.
A key factor driving this enhanced performance is the scaling of inference compute. Discover how scaling inference compute up to 100 million tokens drastically improves AI hacking performance without needing technical sophistication. This substantial computational power allows AI models to process and analyze vast amounts of data, understand complex network configurations, and generate effective attack vectors with unprecedented efficiency.
Critically, this improvement comes without requiring technical sophistication from the user, effectively lowering the barrier to entry for aspiring cybercriminals. The AI handles the intricate technical details, abstracting away the need for deep cybersecurity knowledge or programming skills, making advanced hacking capabilities accessible to a wider range of actors.
The escalating arms race as hacking tools democratize
The implications of AI models gaining autonomous hacking capabilities are far-reaching for cybersecurity. One immediate effect is the intensification of the cybersecurity arms race.
Organizations must now contend with threats that are not only more sophisticated but also potentially faster and more adaptable due to AI’s operational speed and learning capabilities. This demands a corresponding evolution in defensive strategies, potentially leading to increased adoption of Generative AI Versus AI: Creating New Content and AI-powered defense systems that can detect and respond to AI-driven attacks in real-time.
The reduction in required technical sophistication for attackers means a wider array of individuals and groups can now mount effective cyberattacks. This democratization of advanced hacking tools could lead to an increase in the volume and diversity of threats, straining existing security infrastructures and personnel.
Small and medium-sized businesses, which often lack the extensive cybersecurity resources of larger enterprises, may become particularly vulnerable. The economic cost of breaches, already substantial, is likely to rise as attacks become more frequent and potent. Security teams will need to re-evaluate their resource allocation, prioritizing proactive threat intelligence and advanced detection mechanisms over traditional perimeter defenses.
Future adaptive AI threats and defensive countermeasures
The trajectory of AI-powered cyberattacks suggests several critical areas for future observation. The continuous development of frontier AI models, leveraging advancements in hardware like What are NVIDIA AI Chips and Their Role in AI?, will likely lead to even greater autonomy and capability.
We can anticipate AI systems moving beyond executing pre-defined steps to dynamically adapting to defensive measures, learning from failed attempts, and discovering novel vulnerabilities. This will push the frontier of what autonomous AI agents can achieve, mirroring trends seen in other sectors like AI Trading Agents Power Autonomous Retail Finance Trading.
The cybersecurity industry will need to focus on developing equally advanced defensive AI. This includes:
- AI-driven intrusion detection systems
- Automated patch management
- Predictive threat intelligence that can anticipate AI-generated attack patterns
Regulatory bodies and governments will also face the complex task of establishing ethical guidelines and legal frameworks for AI use in both offensive and defensive cybersecurity contexts. The potential for fully autonomous AI agents operating in the cyber domain underscores the urgent need for international collaboration on responsible AI development and deployment, ensuring that the benefits of this technology outweigh the significant security risks it introduces.