Defending Against AI-Driven Attacks
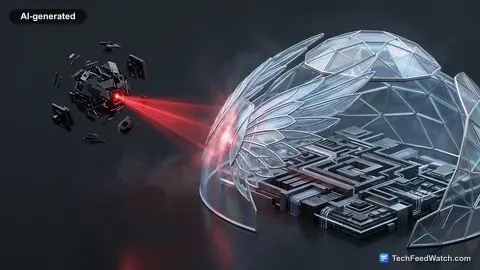
Given the evolving nature of promptware, a fundamental shift in defensive strategy is necessary. IBM Technology recommends adopting an “assume breach” mentality, treating the AI model or agent itself as a potential insider threat.
This approach means securing the environment as if the AI is already malicious, focusing on limiting its capabilities and blast radius. Organizations must restrict an AI’s ability to propagate, move laterally, and leverage permissions it gains from users or the environment.
A significant challenge in defending against promptware lies in visibility. Current logging systems often lack the granularity to capture the subtle interactions or hidden instructions that lead to prompt injections. Developing new logging mechanisms is essential to monitor AI conversations and identify where malicious prompts originate.
Strong Identity and Access Management (IAM) for AI agents is paramount. Understanding which agent performed an action, its assigned permissions, and the model it was built upon can help defenders trace and mitigate misuse.
Drawing parallels to other injection attacks, the core problem often lies in the insufficient separation between instructions and data. While preventing all prompt injections may not be feasible, an in-depth defensive strategy should focus on breaking the kill chain at subsequent steps.
This includes implementing strong telemetry to monitor AI activities, understand what is happening, and quickly assess the impact of a compromise.
Cloud Ecosystems: The Modern Attack Surface
Beyond AI systems, the cybersecurity environment is also witnessing a significant shift in cloud attack trends, moving away from targeting hardened cloud infrastructure to exploiting the broader cloud ecosystem.
Threat actors now focus on:
- Identities
- Integrations
- APIs
- Workflows
- Administrative tools that connect disparate services
This shift makes the “edges” of the cloud a more efficient and scalable target than attempting to breach core cloud services.
The attractiveness of cloud edges stems from the wide-open opportunities for lateral movement once an attacker gains initial access. Cloud environments, by design, often rely on implicit trust and convenience to facilitate the federation of services and reuse of components.
While this enhances usability and allows for rapid deployment, it creates a fertile ground for attackers. They target authentication mechanisms, such as Entra ID linked to Active Directory, to gain authenticated access. Once inside, they can compromise an entire service that has expanded throughout an organization.
Third-party services integrated within cloud environments represent additional access points that often lack the same level of scrutiny as the primary cloud provider’s offerings. The interconnectedness of these services means that a vulnerability in one component can expose others, allowing attackers to pivot and escalate privileges.
Securing the Cloud’s Edges
Effective cloud security requires a renewed focus on foundational principles like zero trust and defense in depth. Organizations must assume that any access attempt could be malicious and verify every user and device before granting access. Implementing multi-factor authentication (MFA) for every login, especially for administrative accounts, is a critical first step.
Given that cloud agents and services often act as highly privileged accounts connecting various data sources, they must be treated with the same rigor as human administrators. Strict monitoring of these accounts, along with proper segmentation and bounding of integrations, is essential to limit potential damage.
While the convenience of cloud services is a major driver for adoption, organizations must carefully weigh this against security implications. Over-reliance on implicit trust can lead to vulnerabilities. A comprehensive strategy involves understanding all access points, continuously monitoring activity, and ensuring that security controls are aligned across hybrid and multi-cloud environments.
The Rusting Edge and Foundational Security
Amidst the advanced threats targeting AI and cloud, there remains a persistent challenge: “cybersecurity’s rusting edge.” This term refers to neglected areas of an organization’s infrastructure where defenses are outdated or insufficient.
This often includes critical operational technology (OT) systems that, while not directly discussed in detail, are mentioned as a key area of concern in the evolving threat environment. These foundational systems, if left unaddressed, can become significant vulnerabilities, providing attackers with alternative entry points or targets for disruption.
Ultimately, securing modern enterprises demands a holistic approach. While understanding novel attack vectors like promptware and the intricacies of cloud ecosystem exploitation is vital, organizations must not lose sight of basic security hygiene and the need to protect all infrastructure, including those often considered “out of sight, out of mind.”
An adaptive defense strategy combines cutting-edge threat intelligence with a steadfast commitment to foundational security principles across all environments.